Federal Contractor Cybersecurity: March 2026 Mandates Compliance Guide
Time-Sensitive: New Cybersecurity Mandates for Federal Contractors Go Live March 2026 – Are You Compliant?
The landscape of federal contracting is continuously evolving, and with it, the imperative for robust cybersecurity. For federal contractors, the clock is ticking. March 2026 marks a pivotal deadline – the effective date for new and enhanced cybersecurity mandates that will fundamentally reshape how businesses engage with the U.S. government. Ignoring these changes is not an option; non-compliance could lead to severe penalties, loss of contracts, and significant reputational damage. This comprehensive guide aims to demystify these critical updates, providing federal contractors with the knowledge and actionable steps necessary to achieve and maintain robust federal cybersecurity compliance.
The Urgency of March 2026: What Federal Contractors Need to Know
The U.S. government, as a primary target for sophisticated cyber threats, is continually strengthening its cybersecurity posture. This heightened focus translates directly to its supply chain – federal contractors. The upcoming mandates, primarily driven by updates to the Cybersecurity Maturity Model Certification (CMMC) program and the Defense Federal Acquisition Regulation Supplement (DFARS), are designed to standardize and enhance the protection of sensitive unclassified information (SUI) and Controlled Unclassified Information (CUI) across the Defense Industrial Base (DIB) and other federal agencies.
The March 2026 deadline isn’t just another regulatory hurdle; it’s a fundamental shift towards a more resilient and secure federal supply chain. Contractors who fail to meet these requirements will find themselves ineligible for new contracts and task orders, placing their business at significant risk. Understanding the specifics of these mandates, particularly those related to federal cybersecurity compliance, is no longer a best practice – it’s a business imperative.
Deconstructing the Mandates: CMMC 2.0 and DFARS Updates
CMMC 2.0: A Streamlined Approach to Cybersecurity Maturity
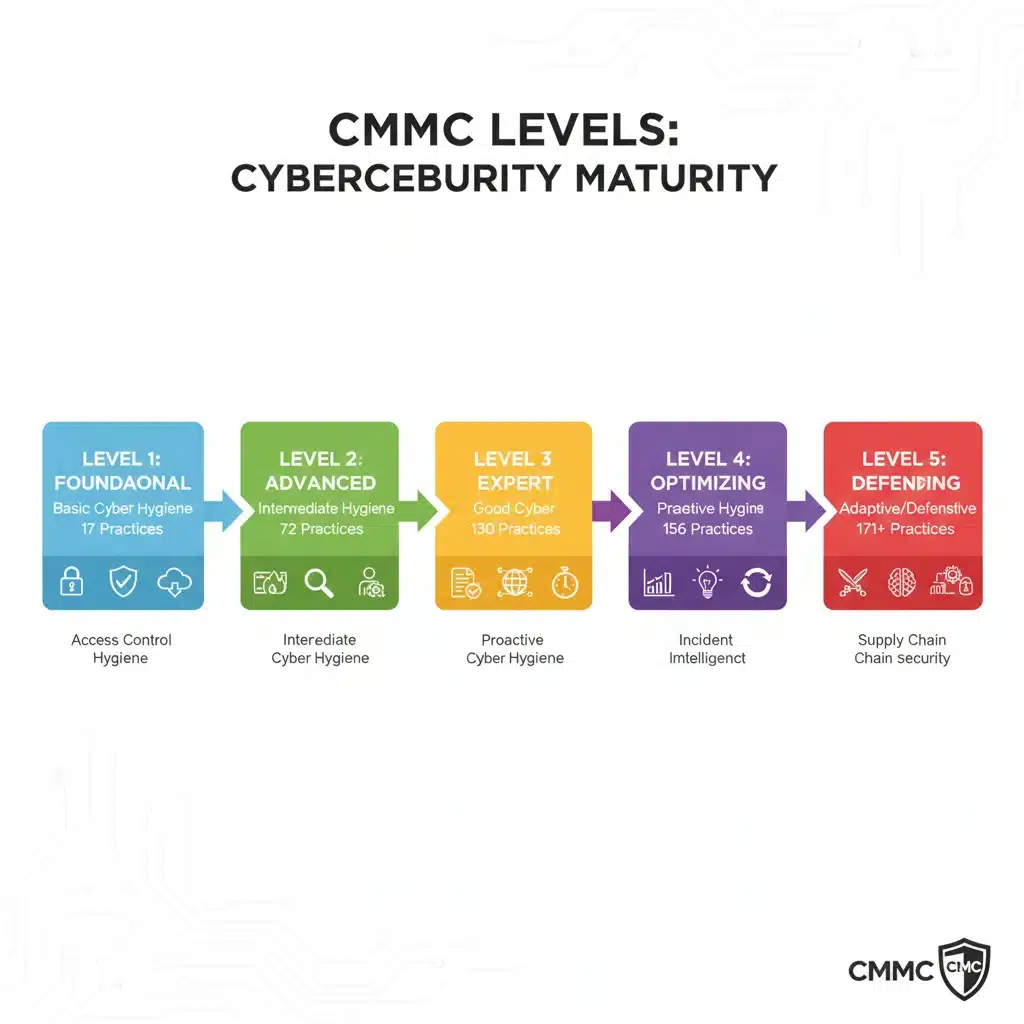
The Cybersecurity Maturity Model Certification (CMMC) program, initially introduced in 2020, has undergone a significant overhaul, resulting in CMMC 2.0. This updated version aims to simplify and streamline the certification process while maintaining the core objective of protecting CUI. CMMC 2.0 moves away from the original five-level model to a more focused three-tiered structure:
- Level 1: Foundational – Focuses on basic cyber hygiene, mirroring the 15 practices of FAR 52.204-21. This level is for companies handling Federal Contract Information (FCI) only.
- Level 2: Advanced – Aligns with the 110 practices of NIST SP 800-171, designed for contractors handling CUI. This level requires triennial third-party assessments for critical programs.
- Level 3: Expert – Based on a subset of NIST SP 800-172 practices, intended for contractors handling CUI on the highest-priority programs. This level requires triennial government-led assessments.
A key change in CMMC 2.0 is the emphasis on self-assessments for Level 1, and for some Level 2 contractors not involved in critical acquisitions. However, for many, third-party assessments (C3PAOs) will still be mandatory, making early preparation crucial. The new framework also introduces a Plan of Action and Milestones (POA&M) process, allowing contractors to address minor deficiencies post-assessment, provided they have a clear plan for remediation.
For contractors, understanding their specific CMMC level requirement is the first step toward achieving federal cybersecurity compliance. This determination is typically made by the contracting officer based on the type of information being handled and the criticality of the program.
DFARS Clause Updates: The Enforcement Mechanism
While CMMC defines the cybersecurity standards, the Defense Federal Acquisition Regulation Supplement (DFARS) clauses provide the contractual teeth. The updated DFARS clauses will incorporate CMMC 2.0 requirements, making adherence to the specified CMMC level a contractual obligation for Department of Defense (DoD) contractors.
Specifically, DFARS Clause 252.204-7012, "Safeguarding Covered Defense Information and Cyber Incident Reporting," has been a cornerstone of cybersecurity requirements for years. However, new DFARS clauses, such as 252.204-7019, 252.204-7020, and 252.204-7021, will explicitly link contract awards to CMMC certification. This means that contractors will need to demonstrate their CMMC certification at the time of contract award for applicable solicitations.
The implication is clear: without the appropriate CMMC certification, contractors will be unable to bid on or win DoD contracts that involve CUI. This direct link elevates federal cybersecurity compliance from a recommendation to a prerequisite for doing business with the DoD.
Understanding Your Information: FCI vs. CUI
A critical first step in navigating these mandates is accurately identifying the type of government information your organization handles. The distinction between Federal Contract Information (FCI) and Controlled Unclassified Information (CUI) dictates the level of cybersecurity required.
- Federal Contract Information (FCI): This is information, not intended for public release, that is provided by or generated for the Government under a contract to develop or deliver a product or service to the Government. It is not CUI. Examples might include routine contract details, project schedules, or administrative communications. Handling FCI typically requires adherence to CMMC Level 1 practices.
- Controlled Unclassified Information (CUI): This is information that the Government creates or possesses, or that an entity creates or possesses for or on behalf of the Government, that a law, regulation, or Government-wide policy requires or permits an agency to handle using safeguarding or dissemination controls. CUI is a broad category and can include sensitive financial data, critical infrastructure information, export-controlled data, privacy information, and more. Handling CUI necessitates adherence to CMMC Level 2 or 3, depending on the criticality.
Misclassifying information can have severe consequences. Under-protecting CUI could lead to security breaches, contractual violations, and legal liabilities. Over-protecting FCI might lead to unnecessary costs and operational inefficiencies. A thorough information assessment and classification process is fundamental to establishing effective federal cybersecurity compliance.
Key Steps to Achieve and Maintain Federal Cybersecurity Compliance
Achieving compliance by March 2026 requires a strategic, phased approach. Here are the essential steps federal contractors should undertake:
1. Understand Your CMMC Level Requirement
Review your existing contracts and solicitations for new work to determine the required CMMC level. If it’s not explicitly stated, engage with your contracting officer or prime contractor to clarify. This will be the foundation of your compliance efforts.
2. Conduct a Gap Analysis Against NIST SP 800-171 (for CMMC Level 2+)
For CMMC Level 2 and above, a comprehensive gap analysis against the 110 controls of NIST SP 800-171 is crucial. This involves evaluating your current cybersecurity practices, policies, and technical controls against each requirement. Identify where your organization meets the standard and where deficiencies exist. This analysis forms the basis for your System Security Plan (SSP) and Plan of Action and Milestones (POA&M).
3. Develop or Update Your System Security Plan (SSP)
Your SSP is a cornerstone of federal cybersecurity compliance. It documents your organization’s security controls, how they are implemented, and how they protect CUI. An accurate and up-to-date SSP is vital for demonstrating compliance during an assessment.
4. Implement Necessary Security Controls and Remediate Gaps
Based on your gap analysis, implement the missing security controls. This could involve technical solutions (e.g., multifactor authentication, encryption, endpoint detection and response), policy updates (e.g., incident response plans, acceptable use policies), and personnel training. Prioritize remediation efforts based on risk and impact.
5. Create and Manage a Plan of Action and Milestones (POA&M)
For any identified gaps that cannot be immediately remediated, develop a POA&M. This document outlines the specific tasks, resources, and timelines for addressing each deficiency. While CMMC 2.0 allows POA&Ms, they must be for minor deficiencies and have a clear path to resolution.
6. Train Your Workforce
Human error remains a leading cause of security breaches. Regular and comprehensive cybersecurity awareness training for all employees is essential. Training should cover topics such as phishing awareness, data handling procedures, password hygiene, and incident reporting protocols.
7. Conduct Internal Audits and Continuous Monitoring
Don’t wait for an external assessment to identify weaknesses. Conduct regular internal audits to ensure your controls are effective and your documentation is current. Continuous monitoring of your systems and networks helps detect and respond to threats promptly, a key aspect of ongoing federal cybersecurity compliance.
8. Prepare for and Undergo CMMC Assessment (if required)
If your CMMC level requires a third-party assessment, engage with an authorized C3PAO well in advance of the March 2026 deadline. The assessment process can be lengthy, so early scheduling is critical. Ensure all documentation (SSP, POA&Ms, policies, evidence of implementation) is readily available.
Challenges and Best Practices for Federal Contractors
While the path to federal cybersecurity compliance is clear, it’s not without its challenges. Small and medium-sized businesses (SMBs) within the DIB often face resource constraints, making compliance particularly daunting.
Common Challenges:
- Resource Constraints: Limited budget, personnel, and expertise.
- Complexity of Requirements: Interpreting and implementing NIST SP 800-171 controls can be intricate.
- Maintaining Documentation: Keeping SSPs, POA&Ms, and evidence of implementation up-to-date.
- Evolving Threat Landscape: The need for continuous adaptation to new cyber threats.
- Supply Chain Risk Management: Ensuring your subcontractors are also compliant.
Best Practices for Success:
- Start Early: Procrastination is your biggest enemy. Begin your compliance journey immediately.
- Leverage Expertise: If internal resources are limited, consider engaging cybersecurity consultants specializing in CMMC and NIST.
- Automate Where Possible: Utilize security tools and platforms that can automate monitoring, vulnerability management, and compliance reporting.
- Foster a Culture of Security: Cybersecurity is everyone’s responsibility. Promote awareness and accountability across the organization.
- Engage Your Supply Chain: Ensure your subcontractors understand their compliance obligations and have mechanisms in place to meet them. Flow down relevant DFARS clauses to lower-tier suppliers.
- Document Everything: "If it’s not documented, it didn’t happen." Maintain meticulous records of your security controls, policies, procedures, and training.
- Stay Informed: The regulatory landscape can change. Regularly check official government sources (e.g., CMMC Accreditation Body, DoD CIO) for updates.
The Cost of Non-Compliance
The consequences of failing to meet the March 2026 mandates are severe and multifaceted:
- Loss of Contracts: The most immediate and impactful consequence. Without the required CMMC certification, contractors will be ineligible for new federal contracts.
- Financial Penalties: Non-compliance can lead to significant fines and penalties, particularly in cases of data breaches involving CUI.
- Reputational Damage: A breach or public finding of non-compliance can severely damage a company’s reputation, affecting future business opportunities even outside federal contracting.
- Legal Liabilities: Failure to protect CUI can result in legal action, including False Claims Act lawsuits, if a contractor falsely represents their compliance status.
- Operational Disruptions: Security incidents due to inadequate controls can lead to costly downtime, data loss, and recovery efforts.
Investing in federal cybersecurity compliance is not merely an expense; it’s an investment in your company’s future, its ability to secure lucrative government contracts, and its overall resilience against cyber threats.
Looking Beyond March 2026: Continuous Compliance
Achieving compliance by the March 2026 deadline is a significant milestone, but it’s not the end of the journey. Cybersecurity is an ongoing process, not a one-time event. The threat landscape is constantly evolving, and so too will the government’s requirements. Federal contractors must embrace a culture of continuous improvement and adaptation.
This means:
- Regular Review and Updates: Periodically review your SSP, policies, and procedures to ensure they remain relevant and effective.
- Threat Intelligence Integration: Stay abreast of emerging cyber threats and vulnerabilities, and adjust your defenses accordingly.
- Security Control Optimization: Continuously evaluate and optimize your security controls to enhance their effectiveness and efficiency.
- Employee Training Refreshers: Conduct annual or semi-annual cybersecurity awareness training to keep your workforce informed about current threats and best practices.
- Engagement with the Community: Participate in industry forums and engage with government agencies to stay informed about future changes to cybersecurity mandates.
By integrating these practices, federal contractors can ensure their federal cybersecurity compliance efforts are sustainable and robust, safeguarding their operations and their ability to serve the government effectively for years to come.
Conclusion: Secure Your Future in Federal Contracting
The March 2026 deadline for new federal cybersecurity mandates, particularly CMMC 2.0 and updated DFARS clauses, represents a critical juncture for all federal contractors. The time for proactive preparation is now. By understanding your specific CMMC requirements, conducting thorough gap analyses, implementing robust security controls, and fostering a strong culture of cybersecurity, your organization can not only achieve compliance but also enhance its overall security posture.
Don’t let non-compliance jeopardize your federal contracts or expose your sensitive data. Embrace these mandates as an opportunity to strengthen your business and reaffirm your commitment to national security. The future of federal contracting belongs to those who prioritize and effectively manage their federal cybersecurity compliance.
If you haven’t started your compliance journey, or if you’re struggling to navigate the complexities, seek expert guidance. The investment in robust cybersecurity now will pay dividends in secured contracts, protected information, and a resilient business for the long term.